

[Nov 29, 2021] New GCCC Exam Dumps with High Passing Rate
Get GCCC Braindumps & GCCC Real Exam Questions
NEW QUESTION 23
Which of the following can be enabled on a Linux based system in order to make it more difficult for an attacker to execute malicious code after launching a buffer overflow attack?
- A. SUID
- B. Iptables
- C. Tripwire
- D. ASLR
- E. TCP Wrappers
Answer: D
NEW QUESTION 24
The settings in the screenshot would be configured as part of which CIS Control?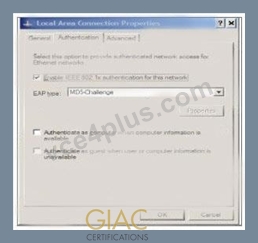
- A. Application Software Security
- B. Inventory and Control of Hardware Assets
- C. Account Monitoring and Control
- D. Controlled Use of Administrative Privileges
Answer: B
NEW QUESTION 25
Implementing which of the following will decrease spoofed e-mail messages?
- A. Internet Message Access Protocol
- B. Network Address Translation
- C. Sender Policy Framework
- D. Finger Protocol
Answer: C
NEW QUESTION 26
Given the audit finding below, which CIS Control was being measured?
- A. Limitation and Control of Network Ports, Protocols and Services
- B. Controlled Use of Administrative Privilege
- C. Controlled Access Based on the Need to Know
- D. Inventory and Control of Hardware Assets
- E. Secure Configurations for Hardware and Software on Laptops, Workstations, and Servers
Answer: B
NEW QUESTION 27
An organization has implemented a control for Controlled Use of Administrative Privilege. The control requires users to enter a password from their own user account before being allowed elevated privileges, and that no client applications (e.g. web browsers, e-mail clients) can be run with elevated privileges. Which of the following actions will validate this control is implemented properly?
- A. Check the log entries to match privilege use with access from authorized users.
- B. Run a script at intervals to identify processes running with administrative privilege.
- C. Force the root account to only be accessible from the system console.
Answer: B
NEW QUESTION 28
Which of the following archiving methods would maximize log integrity?
- A. Magnetic Tape
- B. CD-RW
- C. DVD-R
- D. USB flash drive
Answer: C
NEW QUESTION 29
Which of the following should be used to test antivirus software?
- A. Heartbleed
- B. FIPS 140-2
- C. EICAR
- D. Code Red
Answer: C
NEW QUESTION 30
Which of the following is necessary to automate a control for Inventory and Control of Hardware Assets?
- A. An up-to-date hardening guide
- B. A centralized time server
- C. An inventory of unauthorized assets
- D. A method of device scanning
Answer: D
NEW QUESTION 31
According to attack lifecycle models, what is the attacker's first step in compromising an organization?
- A. Privilege Escalation
- B. Reconnaissance
- C. Initial Compromise
- D. Exploitation
Answer: B
NEW QUESTION 32
Which of the following should be measured and analyzed regularly when implementing the Secure Configuration for Hardware and Software on Mobile Devices, Laptops, Workstations, and Servers CIS Control?
- A. What percentage of systems in the organization are using Network Level Authentication (NLA)
- B. How long does it take to identify new unauthorized listening ports on the network systems
- C. What percentage of assets will have their settings enforced and redeployed
- D. What percentage of the organization's applications are using sandboxing products
- E. How long does it take to remove unauthorized software from the organization's systems
Answer: C
NEW QUESTION 33
An administrator looking at a web application's log file found login attempts by the same host over several seconds. Each user ID was attempted with three different passwords. The event took place over 5 seconds.
* ROOT
* TEST
* ADMIN
* SQL
* USER
* NAGIOSGUEST
What is the most likely source of this event?
- A. An attempt to use SQL Injection to gain information from a web-connected database
- B. An IT administrator attempting to use outdated credentials to enter the site
- C. An automated tool that attempts to use a dictionary attack to infiltrate a website
- D. An attempted Denial of Service attack by locking out administrative accounts
Answer: C
NEW QUESTION 34
Which of the following items would be used reactively for incident response?
- A. A script used to verify patches are installed on systems
- B. An IPS rule that prevents web access from international locations
- C. A phone tree used to contact necessary personnel
- D. A schedule for creating and storing backup
Answer: C
NEW QUESTION 35
A breach was discovered after several customers reported fraudulent charges on their accounts. The attacker had exported customer logins and cracked passwords that were hashed but not salted. Customers were made to reset their passwords.
Shortly after the systems were cleaned and restored to service, it was discovered that a compromised system administrator's account was being used to give the attacker continued access to the network. Which CIS Control failed in the continued access to the network?
- A. Maintenance, Monitoring, and Analysis of Audit Logs
- B. Controlled Use of Administrative Privilege
- C. Incident Response and Management
- D. Account Monitoring and Control
Answer: C
NEW QUESTION 36
Which of the following baselines is considered necessary to implement the Boundary Defense CIS Control?
- A. Network Traffic/Service Baseline
- B. Network Information Flow
- C. Multi-Factor Authentication Standard
- D. Network Device Configuration Baselines
Answer: B
NEW QUESTION 37
What is an organization's goal in deploying a policy to encrypt all mobile devices?
- A. Providing their employees, a secure method of connecting to the corporate network
- B. Applying the principle of defense in depth to their mobile devices
- C. Enabling best practices for the protection of their software licenses
- D. Controlling unauthorized access to sensitive information
Answer: D
NEW QUESTION 38
Which approach is recommended by the CIS Controls for performing penetration tests?
- A. Document a single vulnerability per system
- B. Complete intrusive tests on test systems
- C. Execute all tests during network maintenance windows
- D. Utilize a single attack vector at a time
Answer: B
NEW QUESTION 39
How can the results of automated network configuration scans be used to improve the security of the network?
- A. Reports can be sent to the CIO for performance benchmarks
- B. Results can be included in audit evidence failures
- C. Results can be provided to network engineers as actionable feedback
- D. Scanners can correct network configurations issues
Answer: C
NEW QUESTION 40
An organization has implemented a control for Controlled Use of Administrative Privileges. They are collecting audit data for each login, logout, and location for the root account of their MySQL server, but they are unable to attribute each of these logins to a specific user. What action can they take to rectify this?
- A. Blacklist client applications from being run in privileged mode.
- B. Force user accounts to use 'sudo' f or privileged use.
- C. Turn on SELinux and user process accounting for the MySQL server.
- D. Force the root account to only be accessible from the system console.
Answer: B
NEW QUESTION 41
What type of Unified Modelling Language (UML) diagram is used to show dependencies between logical groupings in a system?
- A. Package diagram
- B. Use case diagram
- C. Class diagram
- D. Deployment diagram
Answer: A
NEW QUESTION 42
An organization has created a policy that allows software from an approved list of applications to be installed on workstations. Programs not on the list should not be installed. How can the organization best monitor compliance with the policy?
- A. Creating an IDS signature to alert based on unknown "User-Agent " strings
- B. Performing regular port scans of workstations on the network
- C. Comparing system snapshots and alerting when changes are made
- D. Auditing Active Directory and alerting when new accounts are created
Answer: A
NEW QUESTION 43
What tool creates visual network topology output and results that can be analyzed by Ndiff to determine if a service or network asset has changed?
- A. Zenmap
- B. CIS-CAT
- C. Netscreen
- D. Ngrep
Answer: A
NEW QUESTION 44
Why is it important to enable event log storage on a system immediately after it is installed?
- A. To allow system to be restored to a known good state if it is compromised
- B. To identify root kits included on the system out of the box
- C. To compare it performance with other systems already on the network
- D. To create the ability to separate abnormal behavior from normal behavior during an incident
Answer: D
NEW QUESTION 45
To effectively implement the Data Protection CIS Control, which task needs to be implemented first?
- A. Employees need to be notified that proprietary data should be protected
- B. The organization's proprietary data needs to be identified
- C. Appropriate file content matching needs to be configured
- D. The organization's proprietary data needs to be encrypted
Answer: B
NEW QUESTION 46
Which of the following assigns a number indicating the severity of a discovered software vulnerability?
- A. CVE
- B. CPE
- C. CVSS
- D. CCE
Answer: C
NEW QUESTION 47
......
GIAC GCCC Exam Syllabus Topics:
| Topic | Details |
|---|---|
| Topic 1 |
|
| Topic 2 |
|
| Topic 3 |
|
| Topic 4 |
|
| Topic 6 |
|
| Topic 7 |
|
| Topic 8 |
|
| Topic 9 |
|
| Topic 10 |
|
| Topic 11 |
|
GCCC Dumps To Pass GIAC Exam in 24 Hours - VCE4Plus: https://www.vce4plus.com/GIAC/GCCC-valid-vce-dumps.html
GIAC GCCC Actual Questions and Braindumps: https://drive.google.com/open?id=1kA4QOwOpgXbzSOxGTl-ApNvqkpppZGUQ