

CS0-002 Dumps for Pass Guaranteed - Pass CS0-002 Exam 2022
CS0-002 Exam Dumps - Try Best CS0-002 Exam Questions from Training Expert VCE4Plus
Prerequisites for Taking the CompTIA CySA+ Certification Exam
CS0-002 has no strict requirements. Anyone, regardless of their knowledge level, can apply to take the test. However, CompTIA does recommend that you have a minimum of 4 years’ experience in the cybersecurity field. Also, the candidates should possess the CompTIA Network+ or CompTIA Security+ certificate or understand everything covered by them.
Security Operations & Monitoring: 25%
- Implementing configuration alterations to current control to enhance security: this module will measure the applicants’ knowledge of permissions, blocklist, firewall, allow list, malware signatures, network access control, Endpoint detection & response, and port security.
- Explaining the significance of proactive threat hunting: this topic includes the skills in establishing hypotheses, threat hunting tactics, bundling critical assets, improving detection abilities, integrated intelligence, minimizing attack surface areas.
- Comparing and contrasting automation technology and concepts: the students will be measured based on their understanding of workflow orchestration, scripting, application programming interface integration, data enrichment, machine learning, and continuous integration, among others.
- Analyzing data as an aspect of security monitoring events: this domain requires your skills in trend analysis, endpoint, e-mail analysis, log review, impact analysis, query writing, network, and security information & event management review.
NEW QUESTION 146
As part of a review of incident response plans, which of the following is MOST important for an organization to understand when establishing the breach notification period?
- A. Legal requirements
- B. Vendor requirements and contracts
- C. Service-level agreements
- D. Organizational policies
Answer: A
NEW QUESTION 147
A security analyst recently discovered two unauthorized hosts on the campus's wireless network segment from a man-in-the-middle attack. The security analyst also verified that privileges were not escalated, and the two devices did not gain access to other network devices. Which of the following would BEST mitigate and improve the security posture of the wireless network for this type of attack?
- A. Enable MAC filtering on the wireless router and create a whitelist that allows devices on the network
- B. Conduct a wireless survey to determine if the wireless strength needs to be reduced
- C. Change the SSID, strengthen the passcode, and implement MAC filtering on the wireless router
- D. Enable MAC filtering on the wireless router and suggest a stronger encryption for the wireless network
Answer: C
NEW QUESTION 148
Approximately 100 employees at your company have received a phishing email. As a security analyst you have been tasked with handling this situation.
INSTRUCTIONS
Review the information provided and determine the following:
1. How many employees clicked on the link in the phishing email?
2. On how many workstations was the malware installed?
3. What is the executable file name or the malware?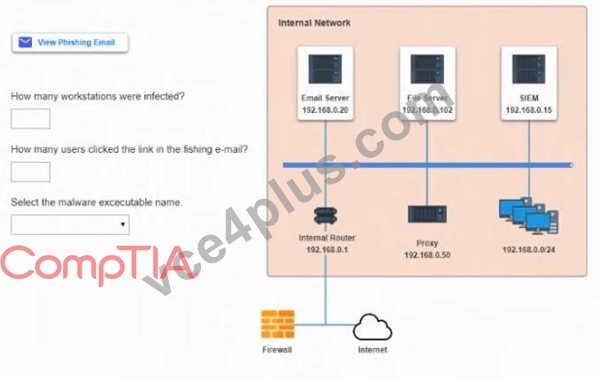
Answer:
Explanation:
see the explanation.
Explanation
Select the following answer as per diagram below.
NEW QUESTION 149
An ATM in a building lobby has been compromised. A security technician has been advised that the ATM must be forensically analyzed by multiple technicians. Which of the following items in a forensic tool kit would likely be used FIRST? (Select TWO).
- A. Crime tape
- B. Chain of custody form
- C. Drive adapters
- D. Drive imager
- E. Hashing utilities
- F. Write blockers
Answer: B,F
NEW QUESTION 150
A user's computer has been running slowly when the user tries to access web pages. A security analyst runs the command netstat -aon from the command line and receives the following output:
Which of the following lines indicates the computer may be compromised?
- A. Line 6
- B. Line 1
- C. Line 5
- D. Line 2
- E. Line 3
- F. Line 4
Answer: F
NEW QUESTION 151
A small electronics company decides to use a contractor to assist with the development of a new FPGA-based device. Several of the development phases will occur off-site at the contractor's labs.
Which of the following is the main concern a security analyst should have with this arrangement?
- A. Making multiple trips between development sites increases the chance of physical damage to the FPGAs.
- B. FPGA applications are easily cloned, increasing the possibility of intellectual property theft.
- C. Moving the FPGAs between development sites will lessen the time that is available for security testing.
- D. Development phases occurring at multiple sites may produce change management issues.
Answer: C
Explanation:
Reference:
https://www.eetimes.com/how-to-protect-intellectual-property-in-fpgas-devices-part-1/#
NEW QUESTION 152
A common mobile device vulnerability has made unauthorized modifications to a device. The device owner removes the vendor/carrier provided limitations on the mobile device. This is also known as:
- A. hashing.
- B. cracking.
- C. jailbreaking.
- D. fuzzing.
Answer: C
NEW QUESTION 153
A security analyst is reviewing vulnerability scan results and notices new workstations are being flagged as having outdated antivirus signatures. The analyst observes the following plugin output:
Antivirus is installed on the remote host:
Installation path: C:\Program Files\AVProduct\Win32\
Product Engine: 14.12.101
Engine Version: 3.5.71
Scanner does not currently have information about AVProduct version 3.5.71. It may no longer be supported.
The engine version is out of date. The oldest supported version from the vendor is 4.2.11.
The analyst uses the vendor's website to confirm the oldest supported version is correct.
Which of the following BEST describes the situation?
- A. This is a true positive, and the new computers were imaged with an old version of the software.
- B. This is a false positive, and the scanning plugin needs to be updated by the vendor.
- C. This is a true negative, and the new computers have the correct version of the software.
- D. This is a false negative, and the new computers need to be updated by the desktop team.
Answer: D
NEW QUESTION 154
Which of the following are essential components within the rules of engagement for a penetration test? (Select TWO).
- A. Authorization
- B. Business justification
- C. List of system administrators
- D. Payment terms
- E. Schedule
Answer: A,E
NEW QUESTION 155
A security analyst is reviewing the following web server log:
Which of the following BEST describes the issue?
- A. Directory traversal exploit
- B. SQL injection
- C. Cross-site scripting
- D. Cross-site request forgery
Answer: A
NEW QUESTION 156
A security analyst has been alerted to several emails that show evidence an employee is planning malicious activities that involve employee PII on the network before leaving the organization. The security analyst's BEST response would be to coordinate with the legal department and:
- A. the human resources department
- B. law enforcement
- C. the public relations department
- D. senior leadership
Answer: A
NEW QUESTION 157
A security analyst has just completed a vulnerability scan of servers that support a business critical application that is managed by an outside vendor. The results of the scan indicate the devices are missing critical patches. Which of the following factors can inhibit remediation of these vulnerabilities? (Choose two.)
- A. Business process interruption
- B. SLAs with the supporting vendor
- C. Inappropriate data classifications
- D. Incomplete asset inventory
- E. Required sandbox testing
Answer: A,E
NEW QUESTION 158
A malicious hacker wants to gather guest credentials on a hotel 802.11 network. Which of the following tools is the malicious hacker going to use to gain access to information found on the hotel network?
- A. tcpdump
- B. Aircrak-ng
- C. Nessus
- D. Nikto
Answer: B
NEW QUESTION 159
A security analyst wants to scan the network for active hosts. Which of the following host characteristics help to differentiate between a virtual and physical host?
- A. Host IPs
- B. DNS routing tables
- C. Reserved MACs
- D. Gateway settings
Answer: C
NEW QUESTION 160
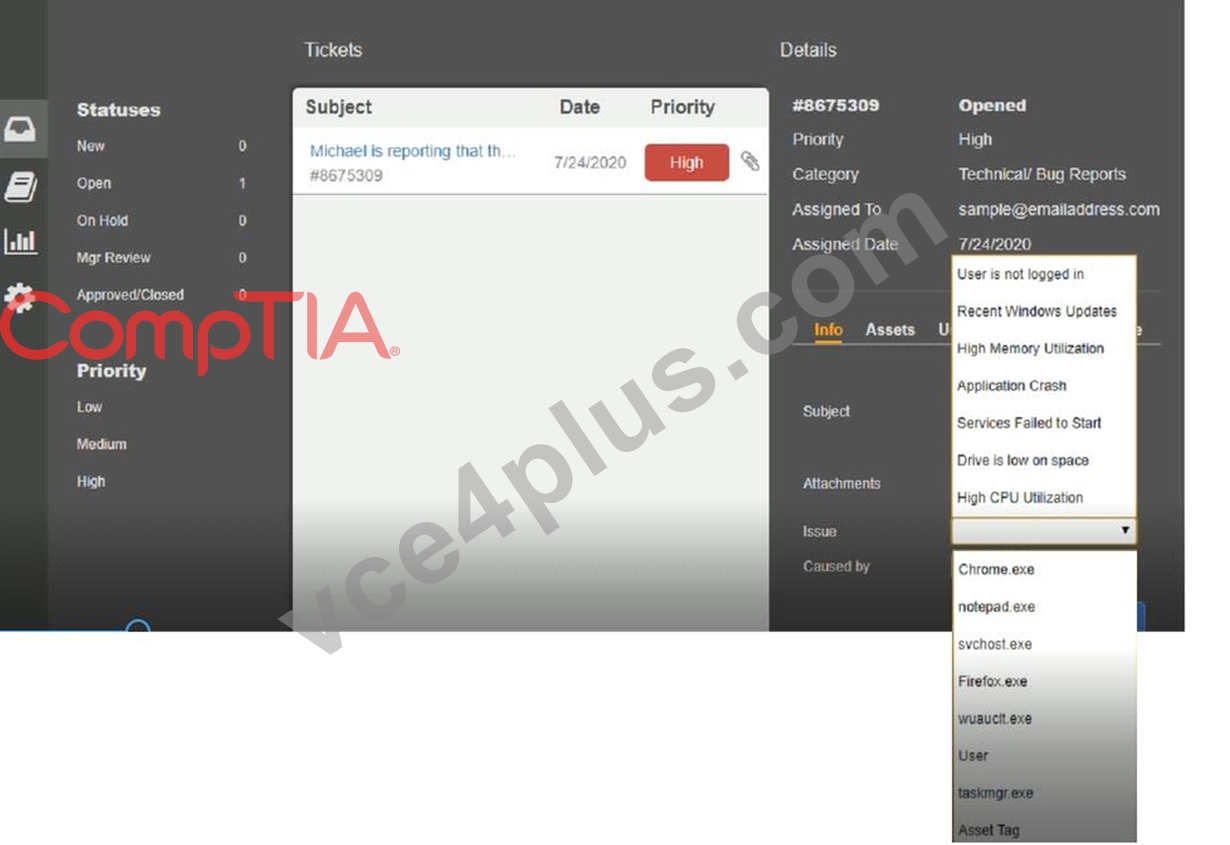
Welcome to the Enterprise Help Desk System. Please work the ticket escalated to you in the desk ticket queue.
INSTRUCTIONS
Click on me ticket to see the ticket details Additional content is available on tabs within the ticket First, select the appropriate issue from the drop-down menu. Then, select the MOST likely root cause from second drop-down menu If at any time you would like to bring back the initial state of the simulation, please click the Reset All button
Answer:
Explanation:
NEW QUESTION 161
An employee at an insurance company is processing claims that include patient addresses, clinic visits, diagnosis information, and prescription. While forwarding documentation to the supervisor, the employee accidentally sends the data to a personal email address outside of the company due to a typo. Which of the following types of data has been compromised?
- A. PCI
- B. PHI
- C. Intellectual property
- D. Proprietary information
Answer: B
NEW QUESTION 162
A system is experiencing noticeably slow response times, and users are being locked out frequently. An analyst asked for the system security plan and found the system comprises two servers: an application server in the DMZ and a database server inside the trusted domain. Which of the following should be performed NEXT to investigate the availability issue?
- A. Review the firewall logs.
- B. Install a WAF in front of the application server.
- C. Perform fuzzing.
- D. Review syslogs from critical servers.
Answer: D
NEW QUESTION 163
Hotspot Question
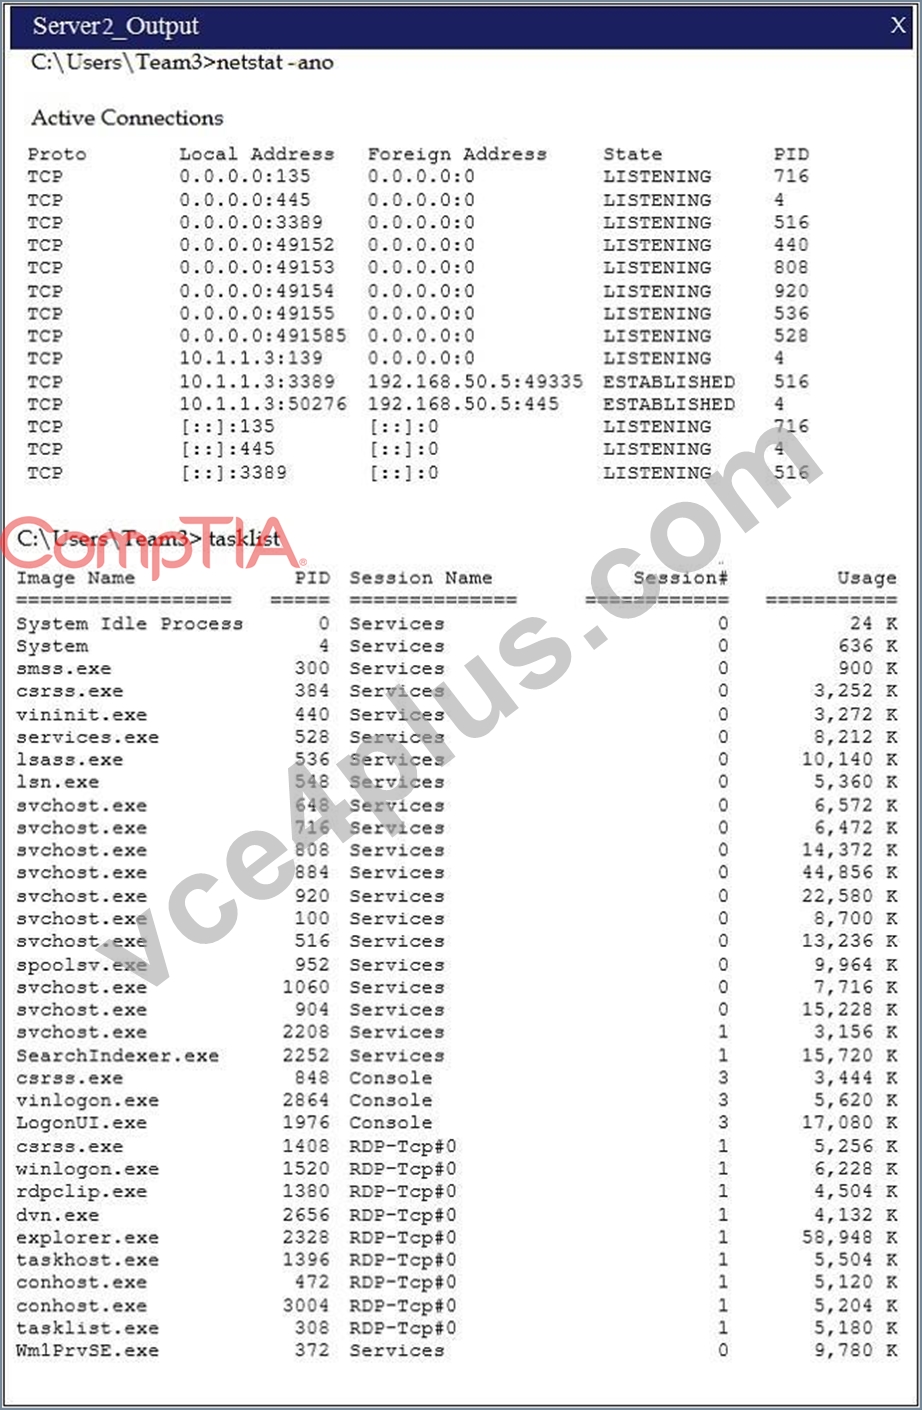
Malware is suspected on a server in the environment. The analyst is provided with the output of commands from servers in the environment and needs to review all output files in order to determine which process running on one of the servers may be malware. Servers 1, 2 and 4 are clickable. Select the Server which hosts the malware, and select the process which hosts this malware.
Instructions:
If any time you would like to bring back the initial state of the simulation, please select the Reset button. When you have completed the simulation, please select the Done button to submit. Once the simulation is submitted, please select the Next button to continue.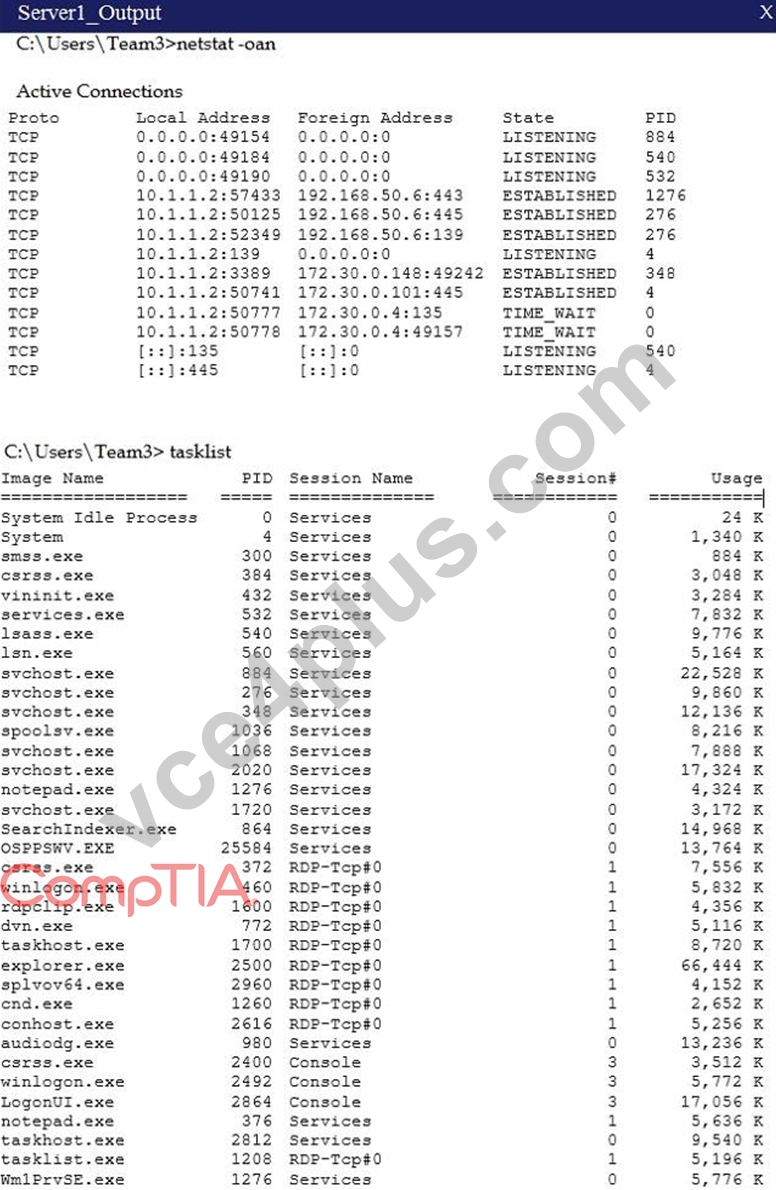
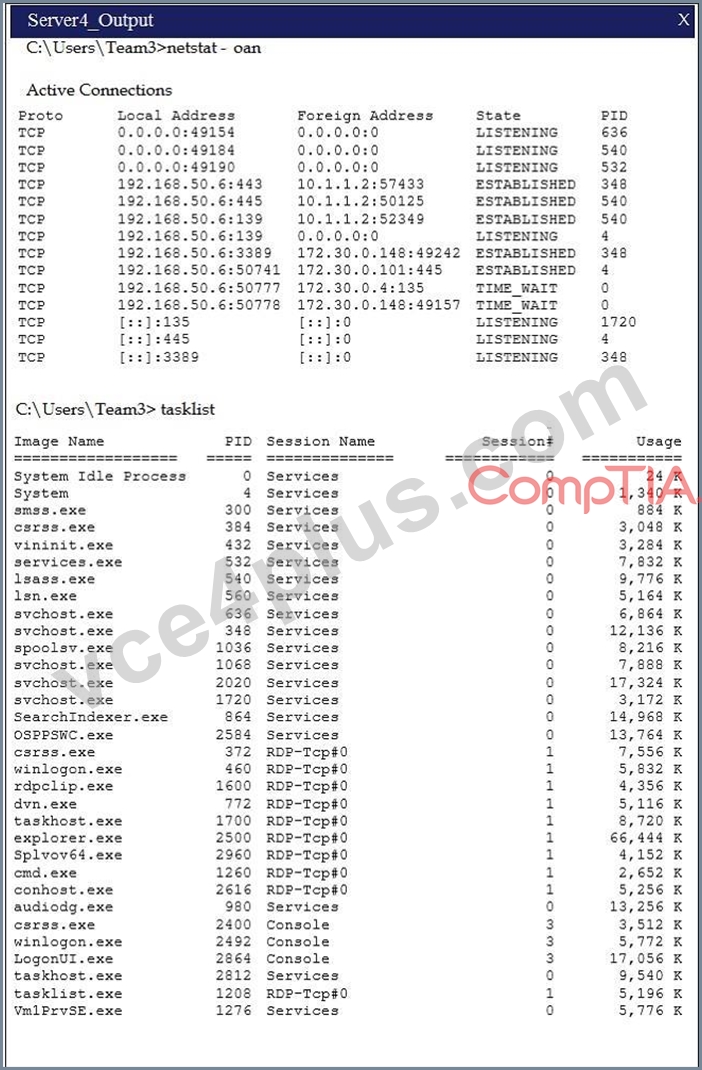
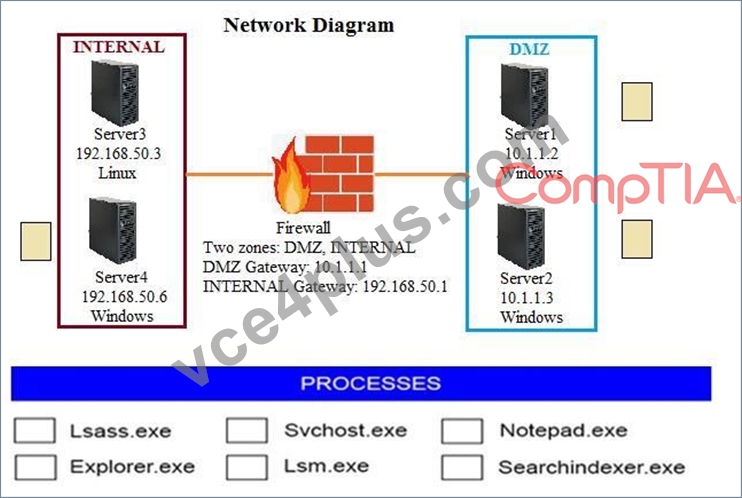
Answer:
Explanation:
NEW QUESTION 164
An analyst is detecting Linux machines on a Windows network. Which of the following tools should be used to detect a computer operating system?
- A. nslookup
- B. nmap
- C. netstat
- D. whois
Answer: B
NEW QUESTION 165
A security analyst received a series of antivirus alerts from a workstation segment, and users reported ransomware messages. During lessons- learned activities, the analyst determines the antivirus was able to alert to abnormal behavior but did not stop this newest variant of ransomware. Which of the following actions should be taken to BEST mitigate the effects of this type of threat in the future?
- A. Installing a firewall between the workstations and Internet
- B. Purchasing cyber insurance
- C. Enabling application blacklisting
- D. Enabling sandboxing technology
Answer: D
NEW QUESTION 166
An organization has not had an incident for several months. The Chief Information Security Officer (CISO) wants to move to a more proactive stance for security investigations. Which of the following would BEST meet that goal?
- A. Advanced antivirus
- B. Active response
- C. Information-sharing community
- D. Threat hunting
- E. Root-cause analysis
Answer: D
NEW QUESTION 167
The business has been informed of a suspected breach of customer data. The internal audit team, in conjunction with the legal department, has begun working with the cybersecurity team to validate the report. To which of the following response processes should the business adhere during the investigation?
- A. The security analysts should not respond to internal audit requests during an active investigation
- B. The security analysts should limit communication to trusted parties conducting the investigation
- C. The security analysts should interview system operators and report their findings to the internal auditors
- D. The security analysts should report the suspected breach to regulators when an incident occurs
Answer: B
NEW QUESTION 168
......
Incident Response: 22%
- Analyzing possible indicators of compromise: this domain includes network-related, host-related, and application-related compromises.
- Using fundamental forensics methods: this objective covers network, Endpoint, mobile, Cloud, virtualization, legal hold, procedures, hashing, carving, and data acquisition.
- Applying the relevant incident response procedure: this subject area covers competence in preparation, detection and analysis, containment, eradication & recovery, and post-incident events.
Latest 100% Passing Guarantee - Brilliant CS0-002 Exam Questions PDF: https://www.vce4plus.com/CompTIA/CS0-002-valid-vce-dumps.html
Practice Examples and Dumps & Tips for 2022 Latest CS0-002 Valid Tests Dumps: https://drive.google.com/open?id=1hrR2GU3x6ND4400vDS3oHxC816qDNzdp