

Steps Necessary To Pass The CS0-002 Exam from Training Expert VCE4Plus
Valid Way To Pass CompTIA CySA+'s CS0-002 Exam
NEW QUESTION 83
Three similar production servers underwent a vulnerability scan. The scan results revealed that the three servers had two different vulnerabilities rated "Critical". The administrator observed the following about the three servers:
- The servers are not accessible by the Internet
- AV programs indicate the servers have had malware as recently as two
weeks ago
- The SIEM shows unusual traffic in the last 20 days
- Integrity validation of system files indicates unauthorized
modifications
Which of the following assessments is valid and what is the most appropriate NEXT step? (Select TWO).
- A. Servers may be generating false positives via the SIEM
- B. Immediately rebuild servers from known good configurations
- C. Servers may have been tampered with
- D. Schedule recurring vulnerability scans on the servers
- E. Activate the incident response plan
- F. Servers may have been built inconsistently
Answer: C,E
NEW QUESTION 84
A company's IDP/DLP solution triggered the following alerts:
Which of the following alerts should a security analyst investigate FIRST?
- A. B
- B. E
- C. C
- D. A
- E. D
Answer: E
NEW QUESTION 85
A cybersecurity analyst is hired to review the security measures implemented within the domain controllers of a company. Upon review, the cybersecurity analyst notices a brute force attack can be launched against domain controllers that run on a Windows platform. The first remediation step implemented by the cybersecurity analyst is to make the account passwords more complex.
Which of the following is the NEXT remediation step the cybersecurity analyst needs to implement?
- A. Move administrator accounts to a new security group.
- B. Deploy a vulnerability scanner tool.
- C. Install a different antivirus software.
- D. Perform more frequent port scanning.
- E. Disable the ability to store a LAN manager hash.
Answer: A
NEW QUESTION 86
What organization manages the global IP address space?
- A. ARIN
- B. WorldNIC
- C. NASA
- D. IANA
Answer: D
NEW QUESTION 87
An information security analyst is compiling data from a recent penetration test and reviews the following output: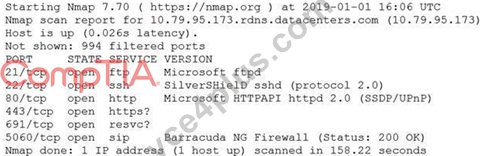
The analyst wants to obtain more information about the web-based services that are running on the target.
Which of the following commands would MOST likely provide the needed information?
- A. tracert 10.79.95.173
- B. ftpd 10.79.95.173.rdns.datacenters.com 443
- C. ping -t 10.79.95.173.rdns.datacenters.com
- D. telnet 10.79.95.173 443
Answer: A
NEW QUESTION 88
A security analyst recently discovered two unauthorized hosts on the campus's wireless network segment from a man-m-the-middle attack.
The security analyst also verified that privileges were not escalated, and the two devices did not gain access to other network devices.
Which of the following would BEST mitigate and improve the security posture of the wireless network for this type of attack?
- A. Conduct a wireless survey to determine if the wireless strength needs to be reduced.
- B. Change the SSID, strengthen the passcode, and implement MAC filtering on the wireless router.
- C. Enable MAC filtering on the wireless router and suggest a stronger encryption for the wireless network,
- D. Enable MAC filtering on the wireless router and create a whitelist that allows devices on the network
Answer: C
NEW QUESTION 89
Given the Nmap request below:
Which of the following actions will an attacker be able to initiate directly against this host?
- A. An SQL injection
- B. ARP spoofing
- C. A brute-force attack
- D. Password sniffing
Answer: C
NEW QUESTION 90
A security analyst is investigating a compromised Linux server. The analyst issues the ps command and receives the following output.
Which of the following commands should the administrator run NEXT to further analyze the compromised system?
- A. kill -9 1301
- B. strace /proc/1301
- C. rpm -V openash-server
- D. /bin/la -1 /proc/1301/exe
Answer: B
NEW QUESTION 91
An organization is moving its infrastructure to the cloud in an effort to meet the budget and reduce staffing requirements. The organization has three environments: development, testing, and production. These environments have interdependencies but must remain relatively segmented.
Which of the following methods would BEST secure the company's infrastructure and be the simplest to manage and maintain?
- A. Create one cloud account with one VPC for all environments.
Purchase a virtual firewall and create granular security rules. - B. Create three separate cloud accounts for each environment.
Configure account peering and security rules to allow access to and from each environment. - C. Create three separate cloud accounts for each environment and a single core account for network services.
Route all traffic through the core account. - D. Create one cloud account and three separate VPCs for each environment.
Create security rules to allow access to and from each environment.
Answer: D
NEW QUESTION 92
A security analyst gathered forensics from a recent intrusion in preparation for legal proceedings.
The analyst used EnCase to gather the digital forensics, cloned the hard drive, and took the hard drive home for further analysis. Which of the following did the security analyst violate?
- A. Virtualization
- B. Chain of custody
- C. Hashing procedures
- D. Cloning procedures
Answer: B
NEW QUESTION 93
A security analyst received a SIEM alert regarding high levels of memory consumption for a critical system. After several attempts to remediate the issue, the system went down. A root cause analysis revealed a bad actor forced the application to not reclaim memory. This caused the system to be depleted of resources.
Which of the following BEST describes this attack?
- A. Memory corruption
- B. Array attack
- C. Injection attack
- D. Denial of service
Answer: A
NEW QUESTION 94
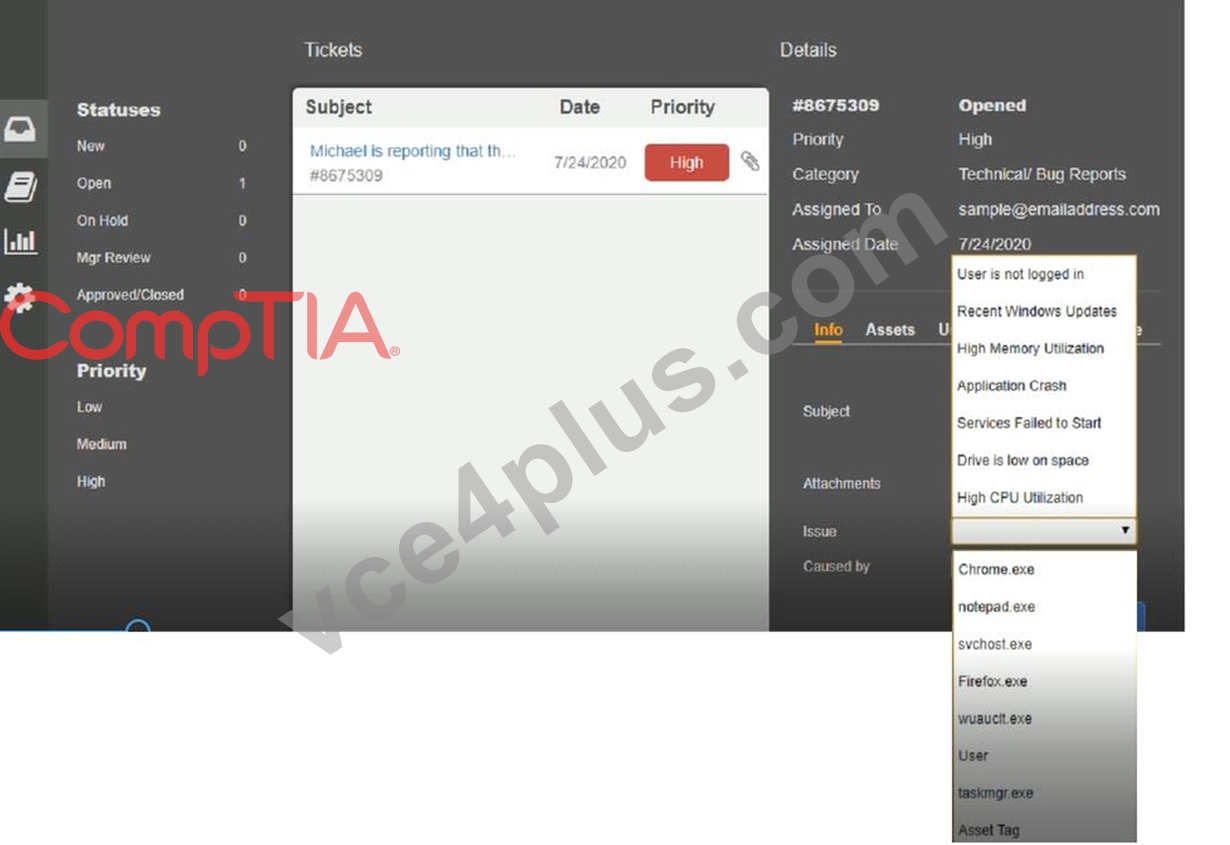
Welcome to the Enterprise Help Desk System. Please work the ticket escalated to you in the desk ticket queue.
INSTRUCTIONS
Click on me ticket to see the ticket details Additional content is available on tabs within the ticket First, select the appropriate issue from the drop-down menu. Then, select the MOST likely root cause from second drop-down menu If at any time you would like to bring back the initial state of the simulation, please click the Reset All button
Answer:
Explanation:
NEW QUESTION 95
A security analyst is conducting a post-incident log analysis to determine which indicators can be used to detect further occurrences of a data exfiltration incident. The analyst determines backups were not performed during this time and reviews the following:
Which of the following should the analyst review to find out how the data was exfilltrated?
- A. Wednesday's logs
- B. Monday's logs
- C. Tuesday's logs
- D. Thursday's logs
Answer: D
NEW QUESTION 96
As part of a review of modern response plans, which of the following is MOST important for an organization lo understand when establishing the breach notification period?
- A. Vendor requirements and contracts
- B. Organizational policies
- C. Legal requirements
- D. Service-level agreements
Answer: C
NEW QUESTION 97
A company's modem response team is handling a threat that was identified on the network Security analysts have as at remote sites. Which of the following is the MOST appropriate next step in the incident response plan?
- A. Capture a forensic image of the memory and disk
- B. Quarantine the web server
- C. Deploy virtual firewalls
- D. Enable web server containerization
Answer: C
NEW QUESTION 98
A security analyst implemented a solution that would analyze the attacks that the organization's firewalls failed to prevent. The analyst used the existing systems to enact the solution and executed the following command:
$ sudo nc -1 -v -e maildaemon.py 25 > caplog.txt
Which of the following solutions did the analyst implement?
- A. Log collector
- B. Honeypot
- C. Crontab mail script
- D. Sinkhole
Answer: A
NEW QUESTION 99
A storage area network (SAN) was inadvertently powered off while power maintenance was being performed in a datacenter. None of the systems should have lost all power during the maintenance. Upon review, it is discovered that a SAN administrator moved a power plug when testing the SAN's fault notification features.
Which of the following should be done to prevent this issue from reoccurring?
- A. Install a third power supply in the SAN so loss of any power intuit does not result in the SAN completely powering off.
- B. Ensure power configuration is covered in the datacenter change management policy and have the SAN administrator review this policy.
- C. Ensure both power supplies on the SAN are serviced by separate circuits, so that if one circuit goes down, the other remains powered.
- D. Install additional batteries in the SAN power supplies with enough capacity to keep the system powered on during maintenance operations.
Answer: C
NEW QUESTION 100
A company was recently awarded several large government contracts and wants to determine its current risk from one specific APT.
Which of the following threat modeling methodologies would be the MOST appropriate to use during this analysis?
- A. Attack vectors
- B. Total attack surface
- C. Diamond Model of Intrusion Analysis
- D. Adversary capability
- E. Kill chain
Answer: D
NEW QUESTION 101
A security analyst wants to confirm a finding from a penetration test report on the internal web server. To do so, the analyst logs into the web server using SSH to send the request locally. The report provides a link to https://hrserver.internal/../../etc/passwd, and the server IP address is
10.10.10.15. However, after several attempts, the analyst cannot get the file, despite attempting to get it using different ways, as shown below.
Which of the following would explain this problem? (Choose two.)
- A. The web server uses SNI to check for a domain name
- B. Requests can only be sent remotely to the web server
- C. The password file is write protected
- D. The web service has not started
Answer: A,C
NEW QUESTION 102
A cybersecurity analyst is reading a daily intelligence digest of new vulnerabilities. The type of vulnerability that should be disseminated FIRST is one that:
- A. enables remote code execution that is being exploited in the wild
- B. affected the organization in the past but was probably contained and eradicated
- C. enables lateral movement and was reported as a proof of concept
- D. enables data leakage but is not known to be in the environment
Answer: A
NEW QUESTION 103
......
All CS0-002 Dumps and CompTIA Cybersecurity Analyst (CySA+) Certification Exam Training Courses: https://www.vce4plus.com/CompTIA/CS0-002-valid-vce-dumps.html
Free Test Engine For CompTIA Cybersecurity Analyst (CySA+) Certification Exam Certification Exams: https://drive.google.com/open?id=1oGv6G9GPAubtCKiNDITHhuesdPRmYU8A